genus perspective
Information sharing needs a named responsibility
HHS’s proposed HIPAA Security Rule update puts attention on how organizations manage information responsibilities. A useful service connection needs clarity about who can receive, use, and protect each piece of information.
A proposal about protection and responsibility
HHS announced proposed HIPAA Security Rule changes in December 2024, seeking to:
“strengthen cybersecurity protections for individuals’ protected health information”
— HHS Office for Civil Rights, December 2024
The proposal summary (opens in a new tab) described more explicit expectations for security practices. In March 2025, the proposed changes were still under consideration; the existing Security Rule continued to apply. HIPAA obligations also depend on an organization’s role, rather than applying identically to every community group.
The practical leadership question is broader than a particular technical control: who is responsible when information moves through a service relationship?
Draw the journey before choosing the channel
Imagine a hypothetical clinic and community program discussing a new support arrangement. Both want to make introductions easier. One person suggests sharing the same information with everyone involved.
Before deciding how, the organizations need to ask why. What does each recipient need to do? Which information is necessary for that purpose? What authority and permissions apply?
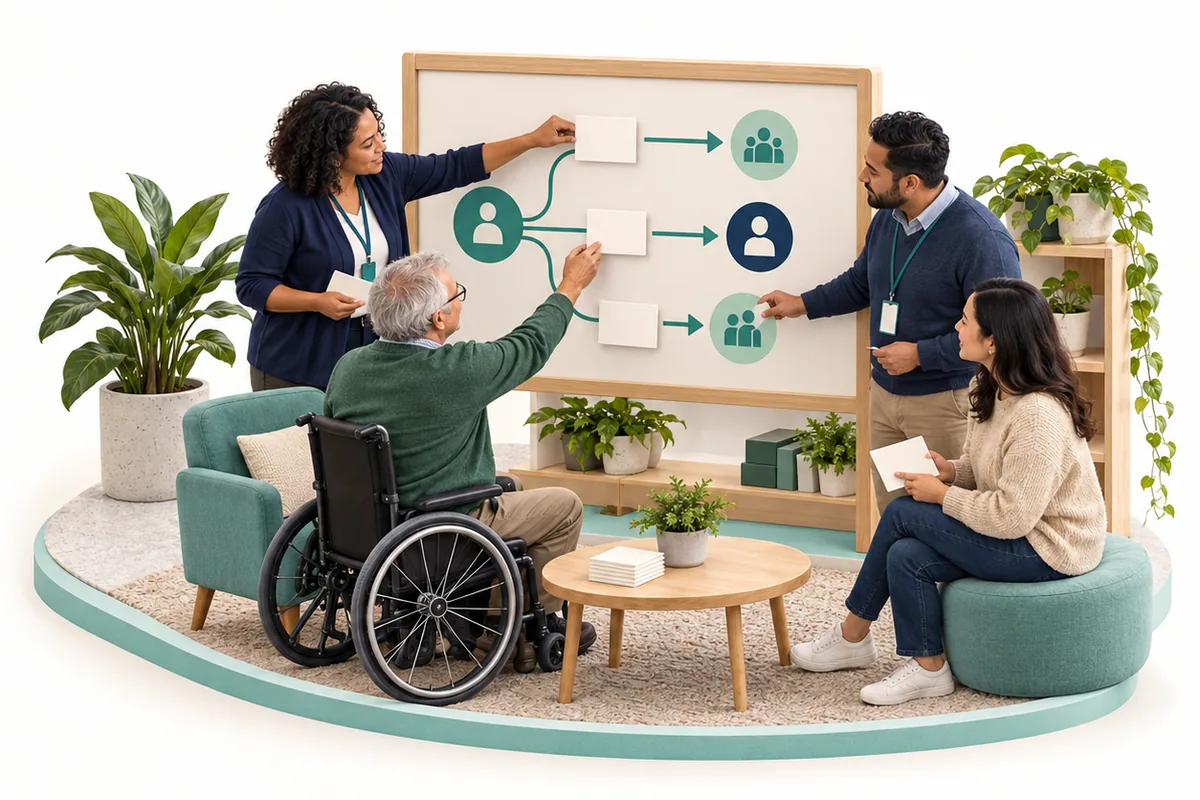
A diagram of the proposed journey can make those questions concrete. It should show responsibilities and decisions, not actual personal records. The participant’s interests belong in that discussion from the beginning.
Give each decision a qualified owner
The colleague making an introduction may not be the person authorized to decide how protected information can be shared. Identify the appropriate privacy, security, legal, and service leads for the arrangement.
Those specialists need a clear description of the work, including the organizations involved and what happens after the first contact. A vague request to “enable collaboration” leaves too much unresolved.
Bring the resulting guidance back into ordinary staff instructions. People carrying out the service should know which route is approved, which information belongs there, and where to ask about an unfamiliar situation.
Plan for changes in people and roles
A relationship does not remain exactly as it was on the day it began. Colleagues leave, responsibilities change, and participants may want a different supporter involved.
Agree how authorized access is reviewed and changed. Name the person or team responsible for acting when the relevant circumstances change.
In our example, a community coordinator’s departure should trigger a defined process. It should not depend on someone remembering every place that colleague might have been included. The same principle applies when a program closes or a supplier relationship ends.
Keep the agreement connected to practice
Written responsibilities are useful only if people can carry them out. Ask how staff learn the approved process and how the organization checks that it remains suitable.
A tabletop discussion using a fictional scenario can reveal uncertainty without exposing personal information. What happens if a message reaches the wrong recipient? Who should be contacted? Which team makes the next decision?
The responsible specialists should define those procedures. The purpose of the service team’s discussion is to identify where instructions are missing or difficult to use, not to improvise security or legal policy.
Explain the arrangement to the person affected
People should receive an understandable explanation of the relevant sharing arrangement through the appropriate process. Ask about their preferences where the arrangement allows choices, and explain any limits accurately.
Do not assume that someone wants every family member involved because they attended one conversation together. Equally, do not make a participant manage the organizations’ internal permissions on their own.
A clear human contact matters when questions arise. Trust is supported by an organization being able to explain its responsibilities, including when a question needs specialist attention.
genus within a defined arrangement today
Configured genus care apps and care walls use audience and permission arrangements to shape experiences. They can provide appropriate updates, conversations, and prepared resources within the organization’s chosen setup.
That does not establish HIPAA compliance or authorize any particular information exchange. Organizations must review their use, responsibilities, contracts, and channels with qualified specialists.
The useful starting point is a defined purpose and an approved process. Technology should support those decisions, with a clear account of who maintains the arrangement as people and services change.
Review the arrangement after a material change, rather than waiting for a problem. A new partner, purpose, or service can alter the information needed and the people responsible for protecting it.
The question before sharing
Can we explain why this recipient needs this information, who authorized the arrangement, and what happens when that responsibility changes?
Supporting references
- HIPAA Security Rule notice of proposed rulemaking (opens reference preview; direct link opens in a new tab)
HHS Office for Civil Rights · 2024-12-27
HHS’s December 2024 proposal considers changes to the HIPAA Security Rule. At the March 2025 reference date, the existing rule remained in effect while the proposal was considered.